Excluding (whitelisting) the Atera Agent keeps your device monitoring and management running smoothly. By excluding the agent paths from antivirus or endpoint protection platforms, you avoid interruptions that could affect its performance and operation, while still maintaining your security standards. This article lists the paths, processes, installer files, and certificates to exclude, with steps for Windows Defender, ESET, SentinelOne, WatchGuard, Sophos, CrowdStrike, Bitdefender, ThreatDown (Malwarebytes), and Palo Alto Cortex XDR.
Paths to exclude
Exclude these paths to ensure smooth sailing for your Atera Agents (v1 and v2) across Windows, macOS, and Linux devices.
Note: Files with randomly generated names (e.g.: $RF4B7L9.msi) are typically Windows Installer cache or temporary files, created by Windows during software installation, update, or repair. EDR and antivirus tools often flag them because the random filename has no established reputation. To confirm whether it relates to Atera, check its location (Atera Agent files live under C:\Program Files\ATERA Networks\AteraAgent\; Windows Installer temp files appear in C:\Windows\Installer\).
Windows
- %PROGRAMFILES%\ATERA Networks (C:\Program Files\ATERA Networks)
- C:\Program Files (x86)\ATERA Networks (on 32-bit systems)
- %WINDIR%\Temp\AteraUpgradeAgentPackage (C:\Windows\Temp\AteraUpgradeAgentPackage)
- %WINDIR%\Temp\Agent.Package.Availability
- %userprofile%\AppData\Local\Temp\TicketingAgentPackage (Helpdesk Agent)
Note: Excluding C:\Program Files\ATERA Networks also covers its subfolders. Some security tools need the specific agent folders instead, as shown in the vendor steps below: C:\Program Files\ATERA Networks\AteraAgent, C:\Program Files\ATERA Networks\AteraAgent\Agent, and C:\Program Files (x86)\ATERA Networks\AteraAgent.
For testing only: consider whitelisting the folder C:\Windows\Installer. After completing the whitelisting process, start another installation, and remove this exclusion once the testing phase is over.
To exclude Nmap for Network Discovery scans, see Nmap Whitelist Guide for Antivirus Software.
macOS
- /Library/Application Support/com.atera.ateraagent
- /Library/LaunchDaemons/com.atera.agent.plist
- /Library/LaunchDaemons/com.atera.ateraagent.plist
- /Library/LaunchDaemons/com.atera.agent.uninstall.plist
- /Applications/AteraAgent.app
- /tmp/com.atera.agent.upgrade/
- /private/tmp/PKInstallSandbox*/Scripts/com.atera.agent*/
Linux
- /usr/lib/atera-agent
- /tmp/atera-agent-upgrade
Processes, installer files, and hashes (Windows)
Process: exclude the Atera Agent process AteraAgent.exe. Tools that use path patterns can exclude the agent executables with C:\Program Files\ATERA Networks\AteraAgent\Agent\*.exe and C:\Program Files (x86)\ATERA Networks\AteraAgent\*.exe.
MSI installer: when downloading the MSI, the file name will be:
- Unassigned installation: "setup.msi"
- Site-specific installation: "setup_{SiteName}.msi"
- Customer-specific installation: "setup_{CustomerName}.msi"
As the file name changes for unassigned, site-specific, or customer-specific installations, please ensure the correct file name is whitelisted.
Hash exclusion: you can also generate a hash (using PowerShell or an application like VirusTotal) for the Atera Agent MSI installer to ensure file-specific exclusions. A hash exclusion is file-specific and independent of the file's name, type, location, or extension.
Whitelist Atera Certificate
If your Anti-Virus or EDR also has a certificate whitelisting feature, you may download the following certificates and configure them.
Steps for specific security tools
The sections below show where to add the Atera exclusions in common antivirus and EDR tools. For more information, please refer to your security software's documentation resources or contact support.
Whitelist Atera in Windows Defender
To whitelist the Atera Agent in Windows Defender, run the following commands in PowerShell with Admin rights. You can run the commands locally using PowerShell ISE (integrated scripting environment). The commands use Add-MpPreference to add path exclusions for C:\Program Files\Atera Networks\AteraAgent, C:\Program Files\ATERA Networks\AteraAgent\Agent, and C:\Program Files (x86)\Atera Networks\AteraAgent, and a process exclusion for AteraAgent.exe.
Add-MpPreference -ExclusionPath "C:\Program Files\Atera Networks\AteraAgent" -Force
Add-MpPreference -ExclusionPath "C:\Program Files\ATERA Networks\AteraAgent\Agent" -Force
Add-MpPreference -ExclusionPath "C:\Program Files (x86)\Atera Networks\AteraAgent" -Force
Add-MpPreference -ExclusionProcess "AteraAgent.exe" -Force
As a preventative measure, you can upload the commands in Atera and run them on your agents. This will stop Windows Defender from flagging and removing the Atera Agent.
Note: Make sure to run the commands as System, and to select the right file type, .ps1.
For more info on uploading scripts to Atera, see Create, upload, and generate scripts
Restore the Atera Agent from Windows Defender quarantine
If Windows Defender quarantined Atera, you'd need to restore Atera and its services. Run the following command using CMD (.bat) with Admin rights. The command runs MpCmdRun.exe -Restore for the detection name HackTool:Win32/RemoteAdmin on the Atera Agent folder.
64-bit machine:
"C:\Program Files\Windows Defender\MpCmdRun.exe" -Restore -Name "HackTool:Win32/RemoteAdmin" -path "C:\Program Files\ATERA Networks\AteraAgent"
32-bit machine:
"C:\Program Files\Windows Defender\MpCmdRun.exe" -Restore -Name "HackTool:Win32/RemoteAdmin" -path "C:\Program Files (x86)\ATERA Networks\AteraAgent"
For more information on restoring files from quarantine, see this article by Microsoft.
Note: In case restoring the Atera Agent is not possible, a full cleanup and reinstallation of the agent should be done. For the cleanup steps, see How do I remove the Atera Agent after my trial has expired?
Whitelist Atera in ESET
To ensure the Atera Agent installs successfully without interference from ESET, add or edit detection exclusions. Whitelist the Windows paths listed under Paths to exclude and the MSI installer file name, or use a hash exclusion, as described under Processes, installer files, and hashes.
Note: ESET won't flag already installed agents.
Detection exclusion. While exclusions can help with false positives, use them cautiously to avoid exposing systems to security risks.
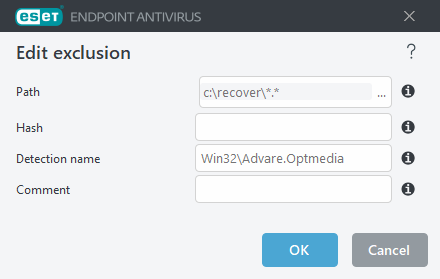
We recommend:
- Limiting exclusions to specific files or directories (via the ellipses button in the Path field).
- Setting exclusions for temporary periods whenever possible.
Note: Exclusions will also apply to the following categories: potentially unwanted applications (PUAs), potentially unsafe applications, and suspicious applications. For more information, see Path exclusion format.
Exclude specific detections. To exclude a detection using its name, provide a valid detection name (e.g., "Win32/Adware.Optmedia"). You can also use the following format directly within the ESET Endpoint Antivirus alert window:
- @NAME=Win32/Adware.Optmedia@TYPE=ApplicUnwnt
- @NAME=Win32/TrojanDownloader.Delf.QQI@TYPE=Trojan
- @NAME=Win32/Bagle.D@TYPE=worm
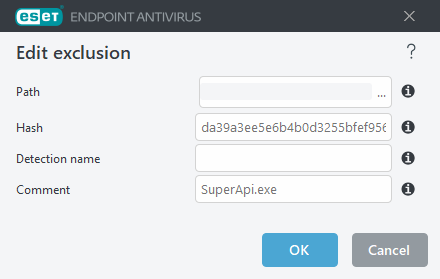
Hash exclusion. If you choose to exclude a file by its hash, the exclusion is file-specific and independent of the file's name, type, location, or extension. You can use the file's SHA-1 hash for this.
Whitelist Atera in SentinelOne
This guide can be used when SentinelOne starts generating false positives about the Atera agent on your devices being malicious. You will need to log into your SentinelOne account to whitelist the Atera agent. Once you have successfully logged in, please follow the steps below:
1. Select Sentinels from the sidebar, then go to the Exclusions tab.
2. Set up the new exclusion by selecting New Exclusion > Create Exclusion.
3. Select the Path option in the New Exclusion window.
4. In the Path field add:
- C:\Program Files\ATERA Networks\AteraAgent
- C:\Program Files (x86)\ATERA Networks\AteraAgent
- C:\Windows\Temp\AteraUpgradeAgentPackage
5. Select Suppress Alerts in the Exclusions mode.
6. Save the changes.
7. Apply it to the devices.
Note: This behavior might occur with older Atera Agent installations. We recommend keeping the Atera Agent up to date via the known installation methods. Additionally, if the SentinelOne alert references a path with \Config.Msi\ and an .rbf file (e.g., \Config.Msi\1d761.rbf), you might need to whitelist that path as well.
Whitelist Atera in WatchGuard
This guide can be used when WatchGuard starts generating false positives about the Atera agent being malicious. You will need to log into your WatchGuard account to whitelist the Atera agent's file path. Once you have successfully logged in, please follow the steps below to configure scan exclusions:
1. In WatchGuard Cloud, select Configure > Endpoints.
2. Select Settings.
3. From the left pane, select Workstations and Servers.
4. Select an existing security settings profile to edit, copy an existing profile, or in the upper-right corner of the page, click Add to create a new profile. The Add Settings or Edit Settings page opens.
5. Enter a Name and Description for the profile, if required.
6. Select General.
7. To exclude a specific file, in the Files text box, type the file name and path to exclude (e.g.: C:\windows\system32\filename.dll). Note: separate multiple entries with commas.
8. To exclude all files in a specific location, in the Folders text box, type a folder path (e.g.: C:\windows\system32, \\192.168.21.23\test, and %ProgramFiles%\Test).
9. Click Save.
10. Select the profile and assign recipients, if required.
For more details, please check the following WatchGuard article.
Whitelist Atera in Sophos
Global Exclusions in Sophos Central allow you to exclude specific files, folders, websites, or applications from being scanned for threats.
1. Log in: Sign in to your Sophos Central account.
2. Open Global Exclusions: Go to: My Products > General Settings > Global Exclusions.
3. Add an Exclusion by clicking Add Exclusion.
4. From the Exclusion Type dropdown, select what you want to exclude (file, folder, website, or application).
5. Enter the path or item details:
- C:\Program Files\ATERA Networks\AteraAgent\Agent
- C:\Program Files (x86)\Atera Networks\AteraAgent
File or Folder (Windows) specifics: you can exclude a full path (drive, folder, or file). Use * as a wildcard for file names or extensions. Note: *.* is not valid.
6. In the Active for dropdown, select when the exclusion should apply: Real-time scanning, Scheduled scanning, or Both.
7. Save your changes.
Notes: Use exclusions cautiously. Overusing them may reduce protection. Double-check paths to avoid incorrect exclusions.
Whitelist Atera in CrowdStrike
Machine Learning Exclusions allow you to prevent specific files or processes from being flagged while still logging events or controlling uploads to the cloud.
1. Navigate to Exclusion Settings: In the Falcon console, go to Configuration > Detections Management > Exclusions > Machine Learning Exclusions
2. Create a New Exclusion by clicking Create Exclusion, then choose whether the exclusion applies to All hosts or specific host groups.
3. Configure Exclusion Details: choose the Exclusion Type:
- Detect/Prevent → Stops detection/prevention but logs events to the cloud.
- Upload to CrowdStrike → Prevents file uploads to the cloud (optional, off by default).
4. Define the Exclusion Pattern for:
- "C:\Program Files\ATERA Networks\AteraAgent\Agent"
- "C:\Program Files (x86)\Atera Networks\AteraAgent"
Use glob syntax to define the pattern, for example C:\Program Files\ATERA Networks\AteraAgent\Agent\*.exe and C:\Program Files (x86)\Atera Networks\AteraAgent\*.exe.
C:\Program Files\ATERA Networks\AteraAgent\Agent\*.exe
C:\Program Files (x86)\Atera Networks\AteraAgent\*.exe
Notes: Apply exclusions only when necessary to avoid reducing protection. Always test exclusions on a small group of hosts before applying globally.
Whitelist Atera in Bitdefender
Exclusions in GravityZone let you prevent certain files, folders, or processes from being scanned. You can add them directly in a policy (Method A) or through configuration profiles for reuse across multiple policies (Method B).
Method A: In-Policy Exclusion
1. Log in to the GravityZone Control Center.
2. Go to Policies and open the policy you want to edit.
3. In the policy menu, navigate to Antimalware > Exclusions. If needed, toggle In-policy exclusions on.
4. From the exclusion type dropdown, select Folder, File, or Process depending on what you need.
5. Enter the full path, use system variables, or apply wildcards. Choose the scanning modules this exclusion should apply to (On-Access, On-Execute/On-Demand, ATC/IDS, Ransomware Mitigation, or All).
6. Add an optional description, then click Add > Save to apply the changes.
Example: To exclude, choose Folder, enter the path, and select the minimum required modules:
- "C:\Program Files\ATERA Networks\AteraAgent\Agent"
- "C:\Program Files (x86)\Atera Networks\AteraAgent"
Method B: Configuration Profile Exclusion
1. Log in to GravityZone.
2. Go to Policies → Configuration profiles and open Exclusions.
3. Click Add Exclusions and select the object type (Folder, File, or Process):
- "C:\Program Files\ATERA Networks\AteraAgent\Agent"
- "C:\Program Files (x86)\Atera Networks\AteraAgent"
4. Click Add → Save.
5. Select the exclusion you created, then click Assign to lists. Choose an existing exclusion list or create a new one.
6. Return to the Policies page, open the policy you want, and go to Antimalware > Exclusions. Enable Exclusions from configuration profiles, select the exclusion list you created, then click Apply > Save.
Notes: Use in-policy exclusions for quick, one-off adjustments. Use configuration profile exclusions if you want consistency across multiple policies. Always start with the minimum modules required to reduce security risks.
Whitelist Atera in ThreatDown / Malwarebytes
You can create exclusions in Malwarebytes either from the Nebula (ThreatDown EDR / Cloud Console) for managed endpoints, or locally in Malwarebytes for Windows. Exclusions prevent specific files, folders, or items from being detected while still protecting the system.
Method A: Nebula (ThreatDown EDR / Cloud Console)
1. Sign in to the Nebula console.
2. In the left menu, go to Configure → Exclusions and click New Exclusion.
3. In the Add Exclusions window:
4. Switch Enable/Disable to On.
5. Enter the path(s) you want excluded (one per line).
- "C:\Program Files\ATERA Networks\AteraAgent\Agent"
- "C:\Program Files (x86)\Atera Networks\AteraAgent"
6. Set Applies to as Global (all endpoints) or choose specific policies.
7. Add a short Comment (who/why).
8. From the Exclusion Type dropdown, select what you’re excluding (File by Path, Folder by Path, MD5 Hash, Registry Key, Website, IP, Command Line, etc.). Wildcards and system variables are supported (e.g. %PROGRAMFILES%, %PROGRAMDATA%, *, **, ?).
9. Click Validate, confirm the entry, then Save.
10. Exclusions will take effect after endpoints sync with the console.
Fast method from an alert: go to Monitor → Detection Center → Detection Log (or Active Detections), select a detection you’ve confirmed as safe, then click Actions → Create Exclusion and follow the prompts.
Method B: Malwarebytes for Windows (local allow list)
1. Open Malwarebytes for Windows.
2. Go to Detection History or Settings → Exclusions (depending on version).
3. Open the Allow List and click Add.
4. Select Allow a file or folder, then browse to the item you want excluded.
5. Choose which detection types to exclude it from (All, Malware/PUP only, Ransomware only).
6. Click Done to apply.
Notes: Use exclusions only after confirming the file, folder, or process is safe. Always start with the narrowest exclusion possible (specific file before folder). In Nebula, global exclusions affect all endpoints, so apply carefully.
Whitelist Atera in Palo Alto Cortex XDR
Exclusions in Cortex XDR can be applied in two ways: an Allow List in a Malware Prevention Profile (specific, recommended), or a Disable Prevention Rule (broader, temporary; use sparingly).
Method A: Add Path to Malware Prevention Profile Allow List
1. In Cortex XDR, go to Endpoints → Policy Management → Prevention → Profiles.
2. Locate the Malware Prevention profile applied to your target endpoints and click Edit.
3. In the profile settings, find Files / Folders in Allow List.
4. Click +Add, enter the full file or folder path you want to exclude, and save the profile.
5. Confirm the profile is attached to the correct Prevention policy for the relevant host groups.
This method excludes a file or folder path from malware examination for endpoints using that profile.
Method B: Create a Disable Prevention Rule
1. In Cortex XDR, open Settings > Exception Configuration > Disable Prevention Rules.
2. Click +Add Rule and choose the platform (e.g., Windows).
3. Enter the Process Name and full path of the executable you want to bypass.
4. Set a time limit (recommended) and define the scope (apply to specific Exception Profiles or all).
5. Enable the rule, save, and ensure the correct Exception Profile is linked to the right endpoints via policy.
This method temporarily bypasses prevention modules for the process you specify. It is useful for urgent false positives during software updates or changes but should be used cautiously.
Notes: Prefer Allow List exclusions for precise, long-term exceptions. Use Disable Prevention Rules only for temporary workarounds, and always with a time limit.


